
How Can Enterprises Let Agents Take Meaningful Action Without Losing Control of Data Access Policies or Risk?
Enterprises can let AI agents take meaningful action without losing control by layering six controls — distinct identity, least-privilege access, permission-aware data retrieval, bounded tool use, human approval gates, and full audit trails — so every agent action is grounded in identity, context, and existing policy.
The stakes changed when agents moved from answering questions to taking action across business systems — a shift Gartner predicts will reach 40% of enterprise applications by the end of 2026, up from fewer than 5% today. A single agent can now query sensitive data, call tools, update records, and trigger workflows at machine speed.
The real challenge is giving agents enough authority to be useful without opening a new path to data exposure or operational risk. A workable model rests on five ideas: distinct identity, least-privilege access, policy-based execution, human approval for high-risk steps, and complete audit trails.
How to let agents take meaningful action without losing control of data, access, policies, or risk
You can let agents take meaningful action by layering six controls instead of relying on one. Each agent gets a clear job, a distinct identity, permission-aware data access, bounded tool use, approval gates for sensitive steps, and a full activity log.
The result is a layered operating model, not a single setting. It combines identity management, data governance, and runtime enforcement that evaluates each request as it happens — and research on multi-agent systems finds that the largest share of failures, roughly 44%, traces to system design rather than model limitations. Static roles alone rarely stay precise enough once an agent starts calling live systems.
Sequence matters. Narrow the problem first, then attach access, policy, and approval controls before you expand autonomy. Good first targets are repetitive workflows with known inputs and measurable outcomes, such as routing support tickets, updating CRM records, or drafting customer follow-ups.
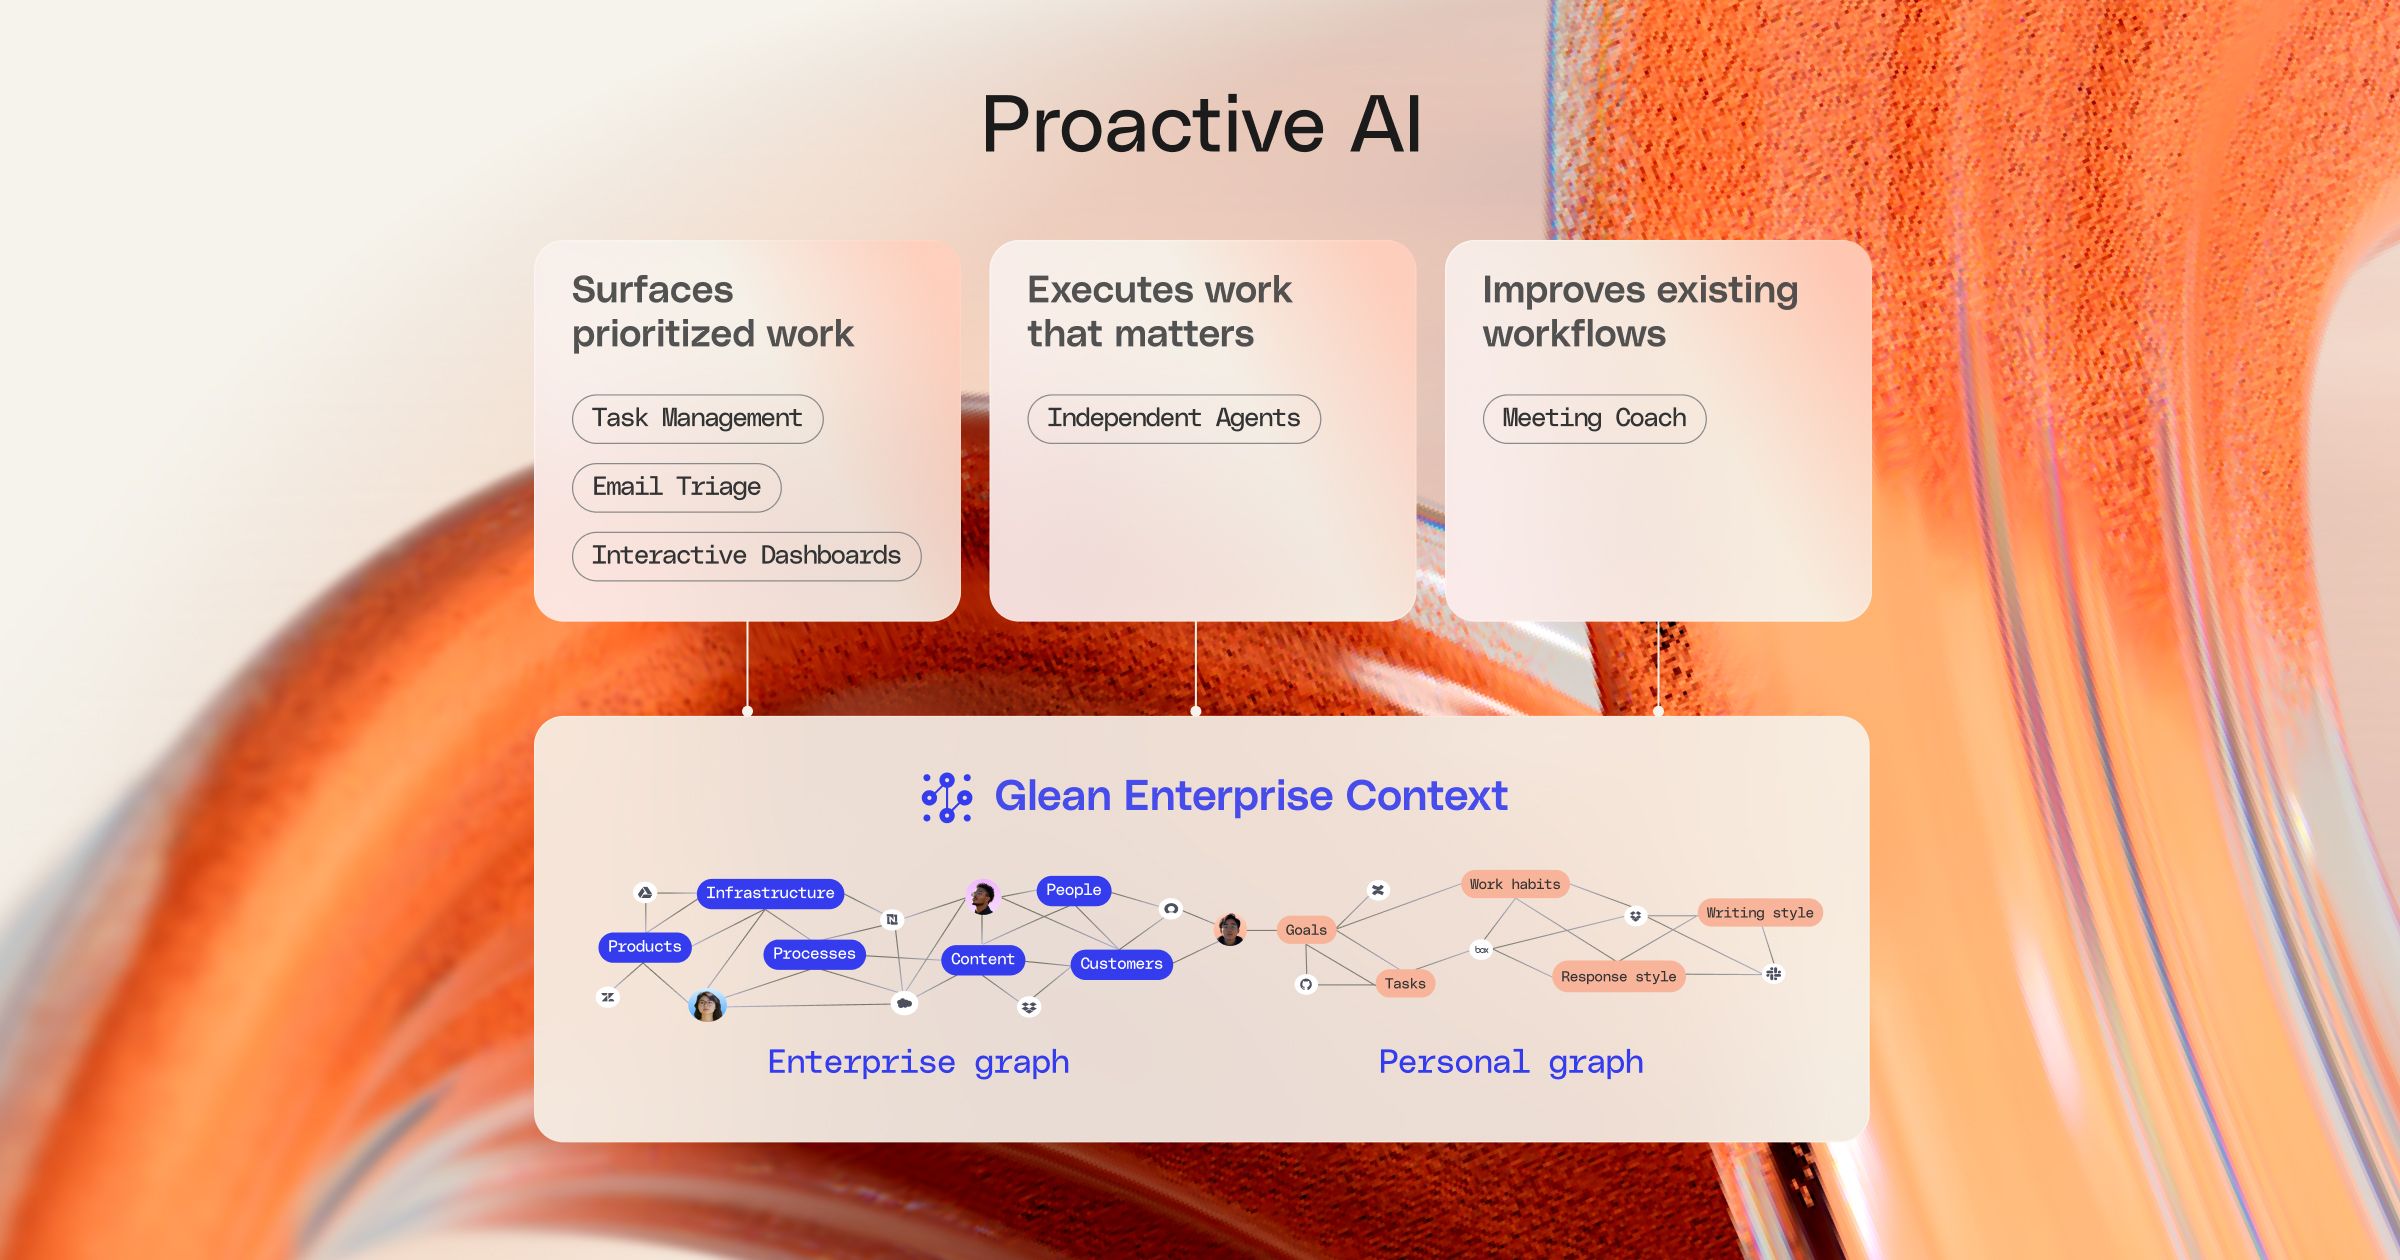
Purpose-built AI agents work best as task-oriented workers with visible execution paths, not open-ended superusers. Glean Agents follow this pattern by respecting permissions enforced upstream of the model, so an agent retrieves only what the requesting user can already see.
1. Define which actions agents should take and how much autonomy each action deserves
Start with the work, not the model. List the workflows where faster execution pays off, then break each one into the exact reads, writes, approvals, and handoffs an agent needs to finish the job. Autonomy should follow the task rather than the reverse.
Sort those actions into tiers, since each one carries a different risk profile. A practical ladder runs from read and summarize, to recommend and draft, to update and trigger, and finally to approve and administer. Reading a resolved support ticket calls for far less control than editing a customer's billing record.
Tie autonomy to reversibility. Reversible, low-impact actions can run on their own, while actions that touch financial data, permissions, production systems, or outbound messages should start under close human supervision.
Document failure modes before launch, not after an incident — in CMU and Salesforce benchmarks, agents completed only about 30–35% of multi-step tasks, so plan for the ones they get wrong. Decide in advance what the agent does when it hits incomplete context, picks the wrong tool, receives a malicious instruction, or reaches data covered by privacy or retention rules. Good first candidates are bounded jobs with measurable results, such as compiling account briefs, reconciling missing fields, or assembling a status update from existing records.
2. Give every agent a distinct identity and bind it to user context correctly
Give each agent its own enterprise identity, with an owner, a stated purpose, a lifecycle, and a revocation path. If you can't attribute an action to a specific agent, governance fails the moment something goes wrong.
Avoid shared service accounts and broad API keys. Distinct identities let you scope access per agent, rotate credentials safely, and trace who initiated each retrieval, tool call, and downstream change.
Decide when the agent acts as itself and when it acts on behalf of a user. That line matters, because user context should shape what the agent can see, retrieve, recommend, and run. Following user permissions best practices, agents that inherit existing user permissions stay inside known access boundaries instead of building a shadow permission model that is harder to audit.
Apply least-privilege access at the identity layer. Grant only the permissions the job requires, keep elevated rights time-bound, and remove unused scopes quickly. Every action then traces back to an approved agent, a user request, and a defined business purpose.
3. Keep data access permission-aware and close to the source
Let agents retrieve from approved systems where permissions already live, rather than copying sensitive content into separate stores with weaker controls. Fewer copies mean fewer policy gaps and less governance drift.
Enforce source-level permissions before information reaches the model or the planner. If a person can't see a document, field, message, or record, the agent shouldn't use it on that person's behalf. Permission-aware retrieval keeps that rule intact at query time.
Push least-privilege access down to the data level: repository, workspace, project, record, field, region, or classification. Coarse access is where most enterprise agent risk begins. Classify sensitive content up front so runtime policies can treat financial data, HR records, legal material, and regulated data differently from general knowledge.
Ground agents in live company knowledge instead of stale exports. Current documents, owners, teams, and workflow state produce better decisions, and they stay inside existing permission boundaries. Treat enterprise AI security as a design choice here, with protected connectors, encrypted transport, and controls that keep sensitive data inside approved boundaries.
4. Limit tools, actions, and system changes with central agent policies
Data access is only half the problem. The other half is tool governance: which systems an agent can call, which objects it can touch, which actions it can run, and in which environment.
Write policy rules that evaluate each request at execution time, using identity, user context, data sensitivity, action type, destination system, timing, and business purpose. Static roles alone rarely stay precise enough once an agent starts calling live systems. Microsoft's cloud governance guidance recommends a single enforceable baseline. It should extend your existing identity, data, and security practices rather than a parallel model built only for AI.
Define allowlists for tools and operations. A support agent might read tickets and draft replies, while an operations agent might open a case, update a status, or trigger a bounded workflow. Neither needs unlimited write access.
Add a policy check between planning and action. An agent can propose a multi-step plan, but validate each step before the next system call runs. Guard against prompt injection too: instructions hidden in retrieved pages, uploaded files, or messages should never rewrite system policy or bypass tool limits.
5. Add proofs, previews, and human approval where the blast radius is higher
Not every action should run the instant an agent decides on it. Require human approval when an agent wants to share sensitive information, delete or overwrite records, change permissions, move money, or modify production systems.
Make the agent show its work first. A useful preview includes the triggering request, the sources used, the policy checks it passed, the exact tool call proposed, and the expected downstream effect. Reviewers then approve, edit, or reject before the final step runs.
Use a draft-first pattern for riskier workflows. Let the agent prepare the response, record update, or workflow package, then route it for sign-off. Add reason codes and business justification for exceptional access, which gives auditors and incident responders a clear record later.
Favor reversible workflows at launch. If an action can be queued, staged, sandboxed, or rolled back, teams learn faster without widening exposure. The agent speeds the work, while the organization keeps control over the moments that carry the highest financial or policy risk.
6. Make every agent action observable, reviewable, and continuously improvable
Log the full chain, not just the final output: user request, agent identity, retrieved sources, policy decisions, tool calls, approvals, outputs, and outcomes. This is where most programs fall short — only 21% of enterprises report a mature governance model for agentic AI. Without that chain, post-incident review turns into guesswork.
Watch for drift in behavior and access. Check whether agents start pulling from new sources, making unusual tool calls, requesting broader permissions, or acting outside the expected pattern for the workflow. Build regular access reviews into the operating model, and revoke connectors or scopes the agent no longer needs.
Track safety and value together. Useful measures include time saved, approval rates, exception volume, policy blocks, false positives, incident count, and the share of work finished without raising risk. Auditable actions and a permission-aware activity log make those numbers trustworthy.
Feed what you learn back into your knowledge foundation. Better metadata, cleaner ownership, and stronger permission hygiene improve both answer quality and safe automation. Mature programs scale by sharpening observability and tightening policy, then expanding autonomy only where the evidence shows the controls hold.
Frequently asked questions about enterprise AI agent governance
What frameworks can enterprises use to govern AI agents effectively?
The most effective approach combines five layers: scoped use cases, a distinct identity for each agent, permission-aware data access, policy-based tool execution, and continuous auditability. It works best as an extension of your existing identity, security, and data governance practices, not a separate control system built only for AI agents.
How can organizations keep data secure while using AI agents?
Keep retrieval close to the source, enforce existing permissions before data reaches the model, limit how much data moves, and apply separate controls for sensitive or regulated content. Data security improves when agents work from approved connectors and live permissions rather than broad exports, copied datasets, or unmanaged memory stores.
What are the best practices for access control with AI agents?
Give every agent its own identity, scope access to the minimum systems and actions the job needs, and separate what the agent does as itself from what it does on behalf of a user. Strong models combine least-privilege access, contextual policy checks, short-lived credentials, and regular reviews of unused or over-broad permissions.
How do enterprises balance operational efficiency with data governance?
Automate the high-volume, low-risk parts of a workflow first, then add approvals only where a bad action would cause real harm. With 88% of organizations now using AI in at least one business function, governance actually speeds adoption, because teams know which workflows are safe to automate, which controls already exist, and where human review still matters.
What policies reduce the risk of AI agents?
Core agent policies define approved data sources, allowed tools, action tiers, approval thresholds, logging requirements, retention rules, incident response, and escalation paths. Risk management improves when the policy language is specific enough to enforce at runtime, not just broad enough to read well in a document.
The enterprises that get the most from agents are the ones that pair meaningful action with real control, one layer at a time. We built our Work AI platform to enforce your existing permissions, keep every action auditable, and let agents act only within the policies you set. Request a demo to see how we can put governed agents to work across your business.